
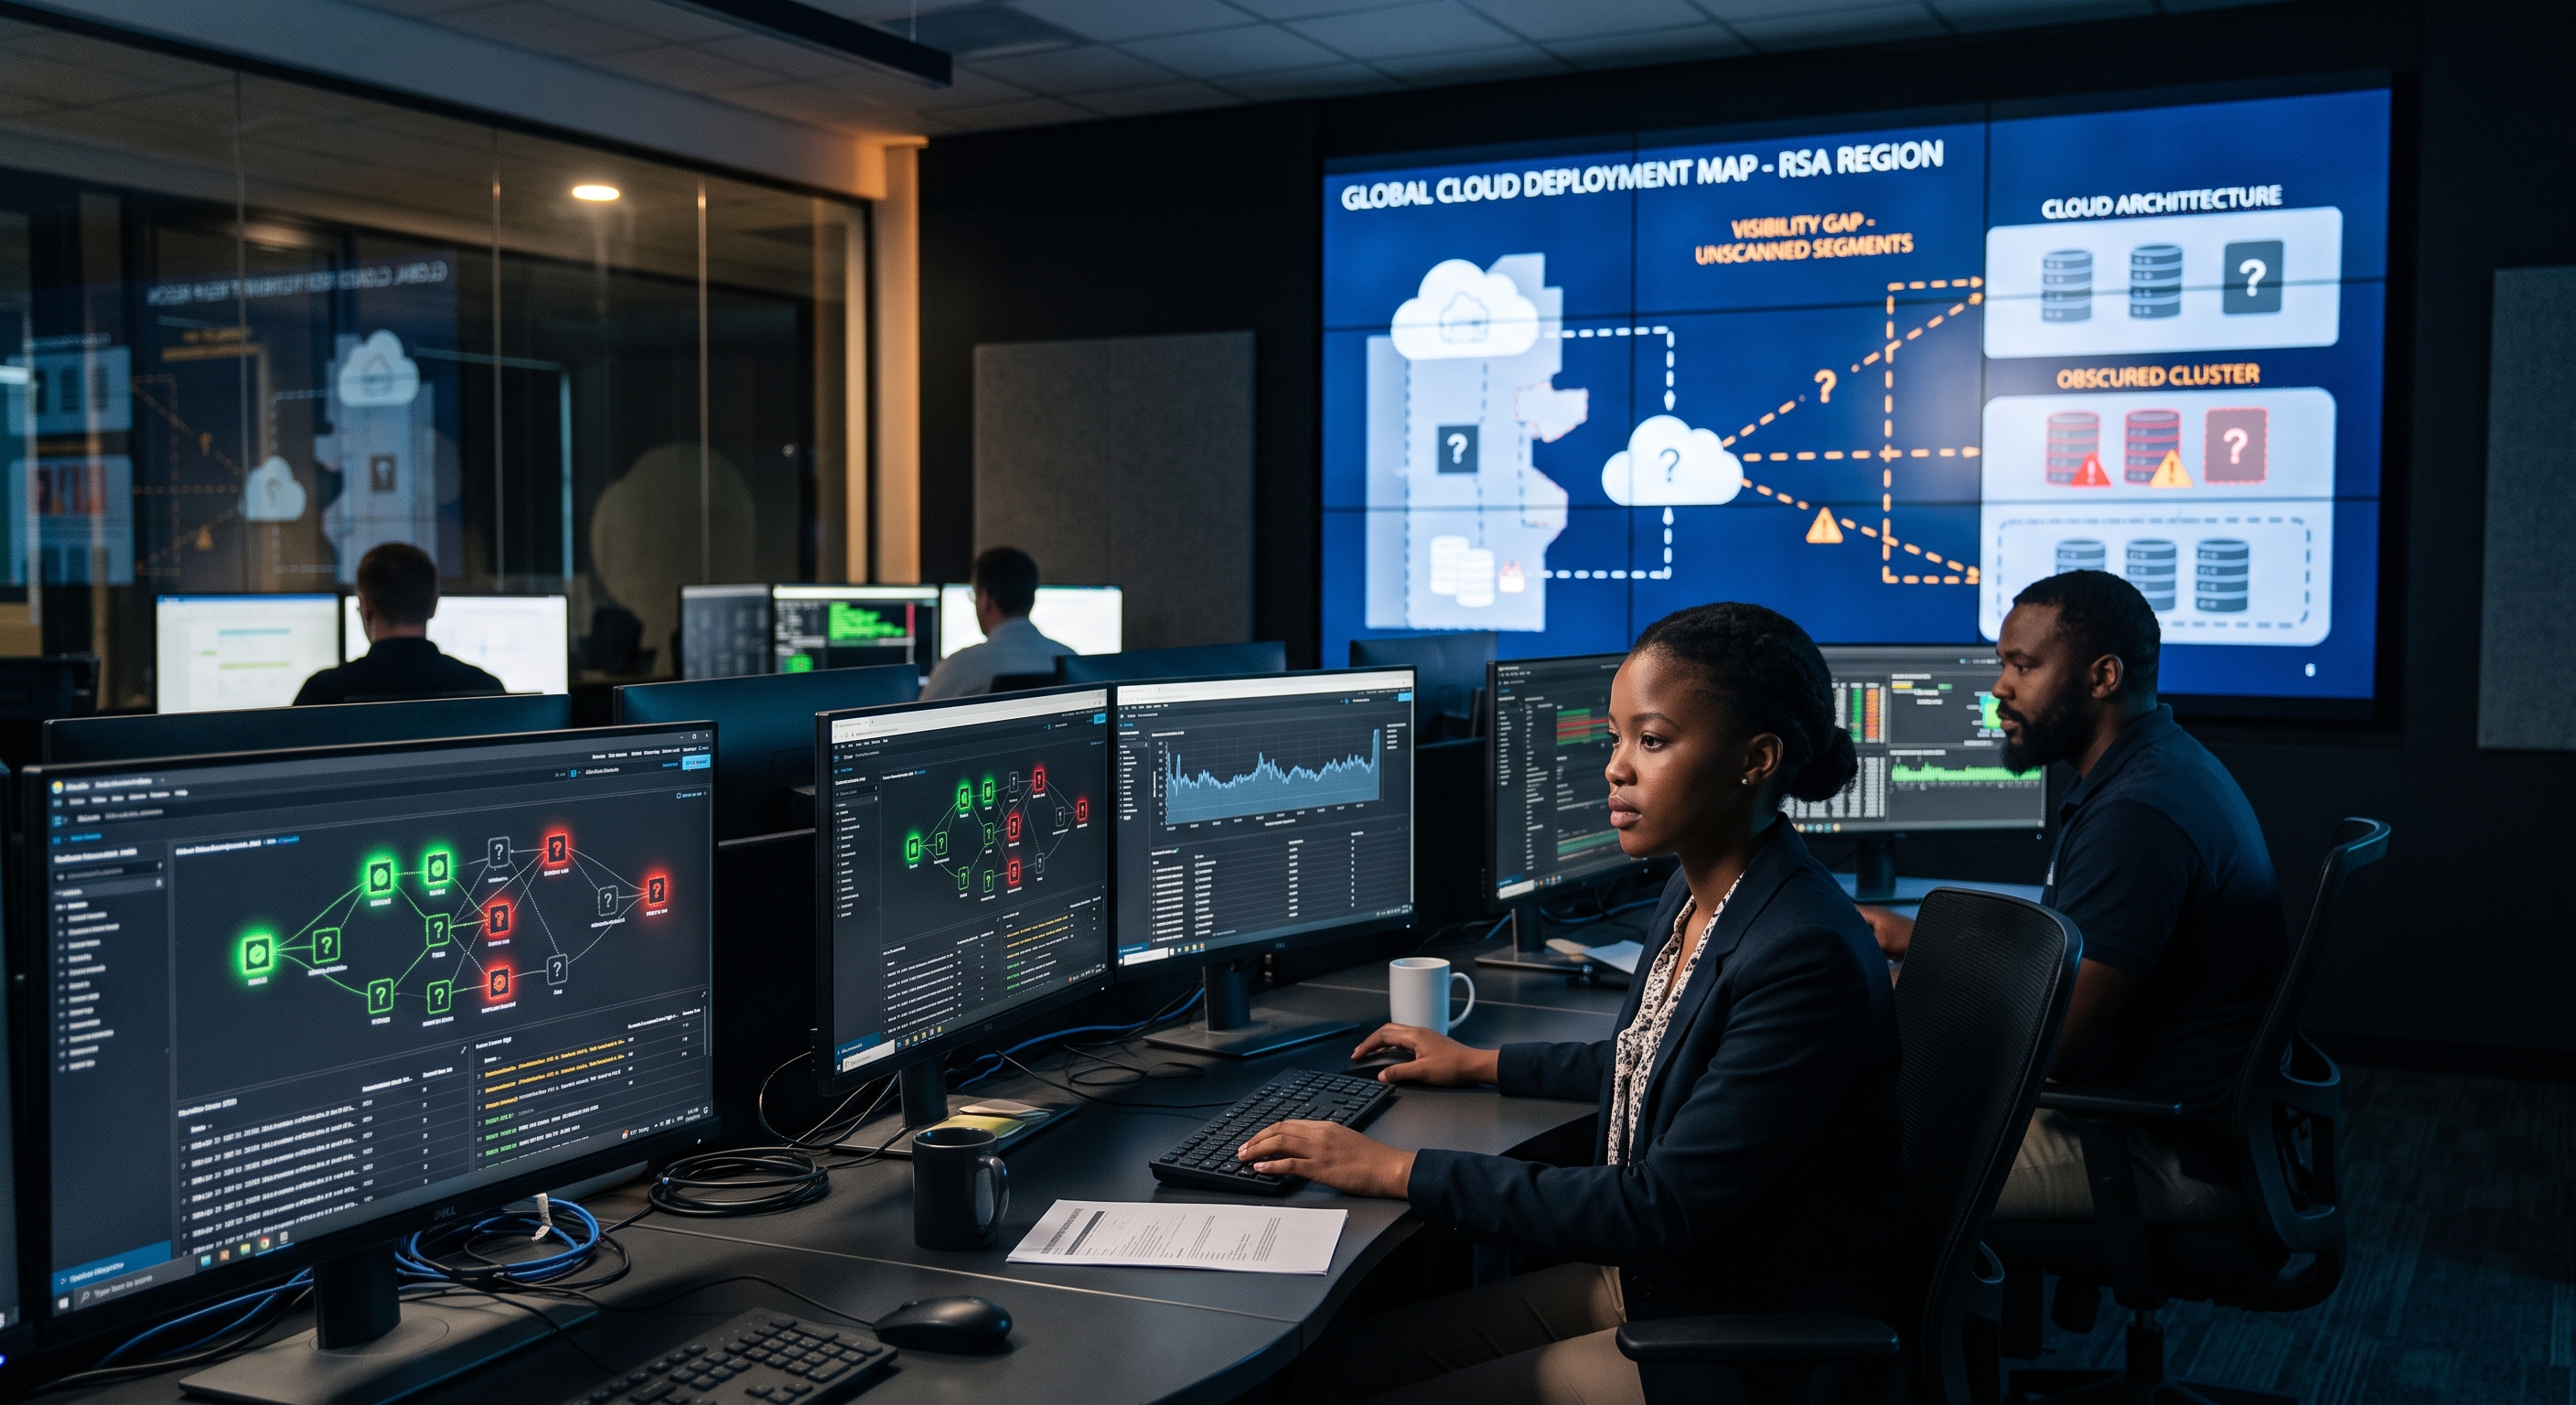
The Visibility Crisis in South African Cloud Security
Artificial intelligence adoption is accelerating across South African businesses. Cloud platforms power these initiatives. Yet according to Accenture's State of Cybersecurity research (August 2026), only 18% of South African organisations have full visibility into their cloud security configurations. That means 82% of organisations are operating with significant security blind spots.
This is not a technical inconvenience. It is a direct business liability. When you cannot see what is happening in your cloud environment, you cannot manage risk—you are accepting it.
Why Visibility Matters: The AI Acceleration Factor
AI is evolving faster than most South African organisations can secure it. Accenture found that only 44% of technology leaders acknowledge that AI is advancing faster than their organisations' cybersecurity capabilities. The gap is real and widening.
Cloud environments are where this gap becomes most dangerous. Digital transformation and AI initiatives rely heavily on cloud platforms. But without visibility into cloud security configurations and approved baselines, organisations are building AI systems on foundations they cannot inspect.
Consider a financial services firm scaling a machine learning model to detect fraud. The model lives in the cloud. Data flows through cloud infrastructure. If the organisation lacks visibility into how that cloud environment is configured—which networks are exposed, which access controls are enforced, which data is encrypted—then the AI system itself becomes a liability rather than an asset.
The Governance Gap: Why Most Organisations Fail
It is not that cloud security tools do not exist. They do. The problem is governance.
According to Accenture's research, just 6% of South African organisations have approved security baselines in place for their cloud environments. A security baseline is a documented standard for what 'secure' looks like in your specific environment. Without it, every team member, every deployment, every configuration decision is made in isolation.
This compounds across large organisations. One team deploys a database without encrypting backups. Another team opens an API endpoint to troubleshoot an issue and forgets to close it. A third team uses shared credentials for administrative access. Each decision seems minor in isolation, but together they create a patchwork of vulnerabilities.
The result: fragmentation, inconsistency, and blind spots.
A Concrete Example: The Real Cost of Invisibility
Imagine a South African retailer running customer data in AWS. They have multiple business units, each deploying applications independently. The head office thinks they have cloud security covered. But:
- The e-commerce team has encrypted data in transit but not at rest
- The logistics system is accessible from the public internet with minimal authentication
- The finance team has three database administrators sharing one administrative password
- No one has a complete inventory of where customer data actually lives
A breach occurs. The retailer discovers that customer payment information was exposed for six months. The investigation reveals that visibility gaps made it impossible to detect the breach earlier. Regulatory fines follow. Customer trust erodes. The cost is not just financial—it is existential.
Without visibility, you cannot detect. Without detection, you cannot respond. Without response, you cannot recover.
What Security Foundations Must Be Built First
Before scaling AI or accelerating digital transformation, organisations must establish three core foundations:
1. Inventory and Asset Visibility
You cannot secure what you do not know you have. This means cataloguing every cloud resource, every data store, every network connection. This is not a one-time exercise—it is ongoing. Cloud environments change continuously.
2. Configuration Standards and Baselines
Define what 'secure' looks like for your organisation. Which encryption standards will you enforce? Which access control models will you use? Which monitoring and logging will be mandatory? Document it. Make it non-negotiable. Audit against it. Just 6% of SA organisations have done this—you can be in that group.
3. Continuous Monitoring and Governance
Visibility without action is useless. Implement tools and processes that continuously monitor cloud configurations against your baselines. Detect drift. Alert on violations. Enforce remediation. Make governance operational, not aspirational.
These foundations are not glamorous. They do not build features. But they enable everything else safely.
The Human Element: Skills and Training
Technology alone does not solve this problem. Your organisation needs people who understand cloud security architecture, identity management, data governance, and compliance frameworks. These skills are in short supply globally and locally.
This is where structured corporate cybersecurity training becomes essential. Whether through formal cyber security courses in South Africa that build foundational knowledge, or advanced corporate training programmes tailored to your industry and infrastructure, upskilling your internal teams directly improves visibility and governance maturity.
For individual learners, career pathways in cloud security are increasingly valuable. Entry-level cyber security short courses offer accessible starting points; advanced programmes build specialisation. For executives and HR managers responsible for Skills Development Levy recovery and B-BBEE skills development scoring, investing in structured cybersecurity training creates measurable, auditable capability improvements while reducing organisational risk.
Melsoft Academy offers QCTO-accredited cybersecurity programmes addressing these exact gaps, with content tailored to South African organisations operating in regulated industries and complex cloud environments.
What to Do Next
Start with an honest assessment. Do you have full visibility into your cloud security configurations? Can you articulate your security baselines? Are you monitoring continuously? If the answer is no to any of these, that is your priority.
Next, assess your team's skills. Who on your staff understands cloud security architecture? Who can design secure data governance? Who can audit and enforce baselines? Gaps here are gaps in execution.
Finally, treat cloud security as a business programme, not a technical checkbox. Assign clear accountability. Set milestones. Measure progress. The organisations that will thrive in the AI era are not those with the most advanced AI systems—they are those with the most mature security governance.
Your cloud visibility is not a luxury. It is a prerequisite for everything else. Build it first. If your team needs to close capability gaps, QCTO-accredited training programmes designed for cybersecurity professionals can accelerate that process.